Red Team
Offensive security research - malware development, EDR evasion, credential theft, and adversary tradecraft notes.
Latest
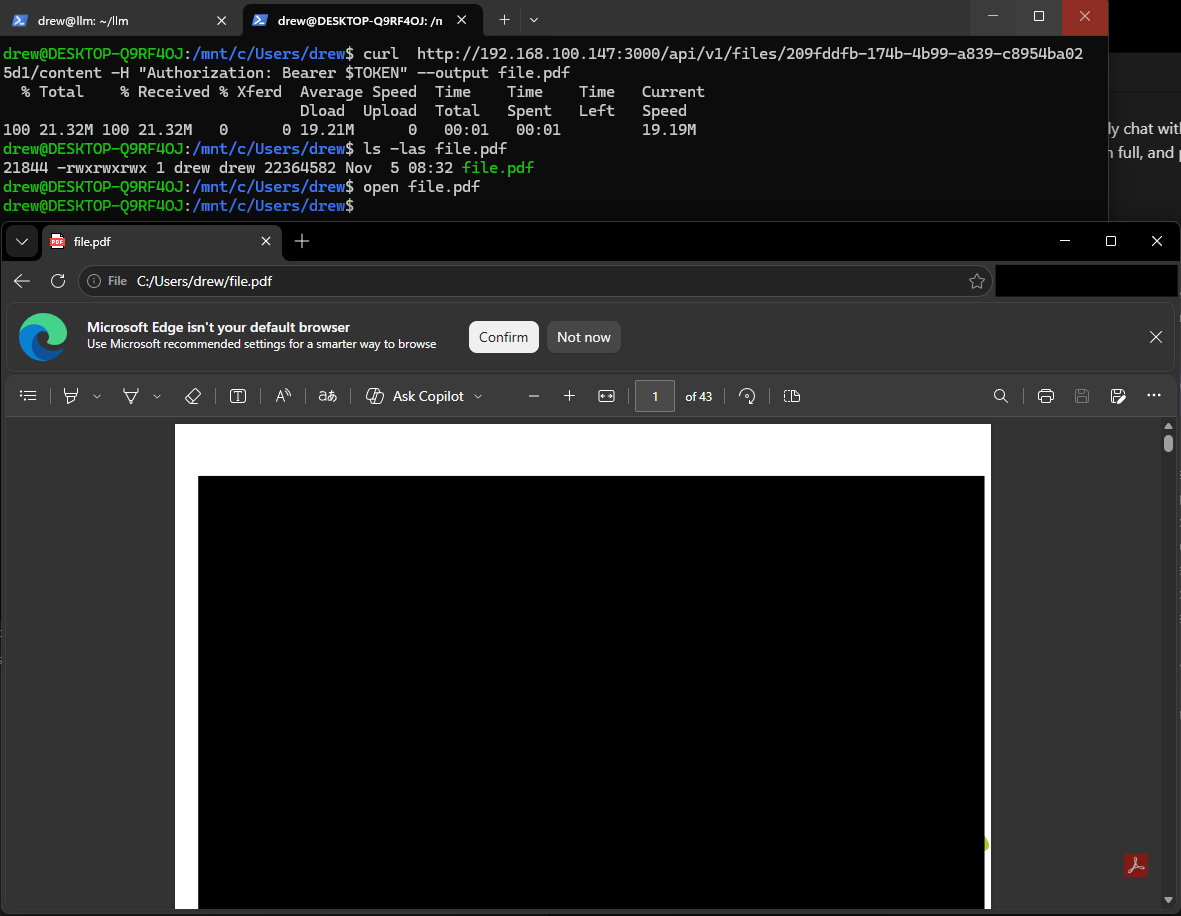
OSINT Enrichment and Knowledge Base Enumeration with Open WebUI
Build a local Open WebUI RAG lab for OSINT on public PDFs, then enumerate the knowledge base and dump documents via API and model tools.
Read post ->Series
Series in this section
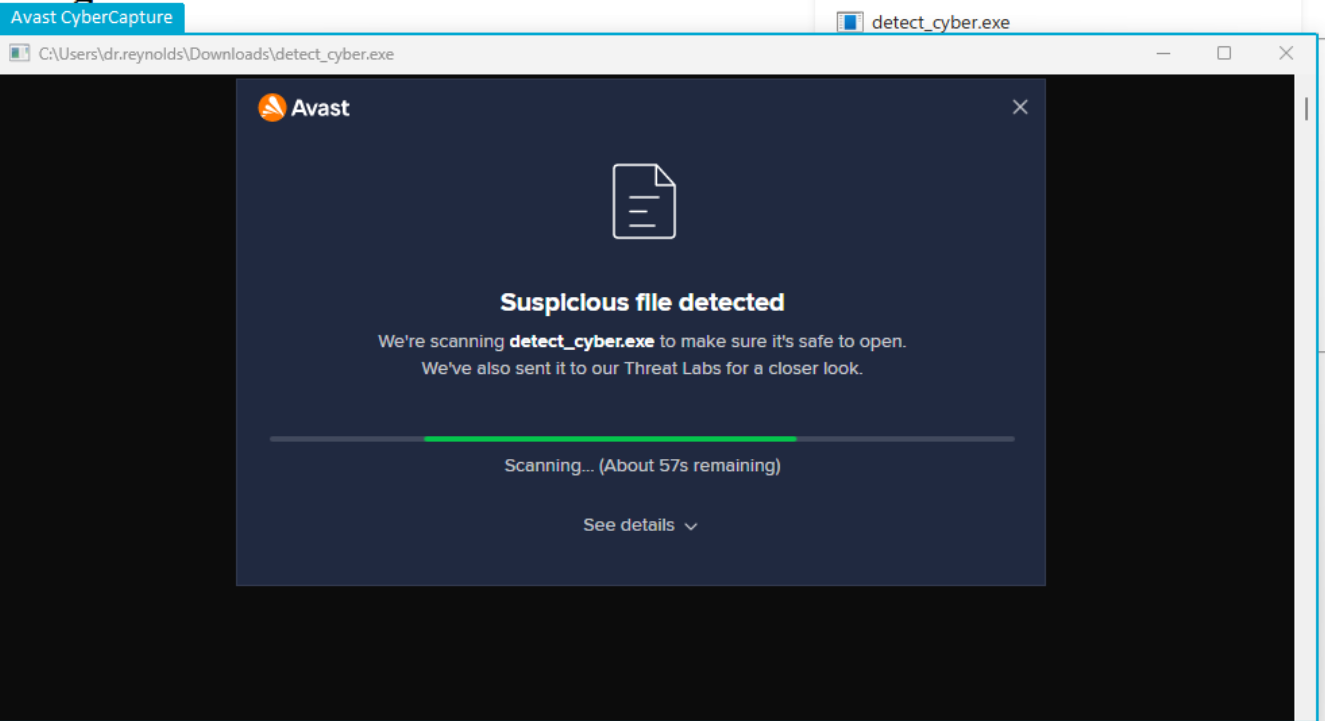
Avast CyberCapture
Techniques for detecting Avast CyberCapture sandboxes through window classes and distinctive strings in process memory.
EDR-Evasive Profile Stealer
Architecture, build-time backends, bypass methods, and extraction techniques (Windows off-screen, CDP, Linux Ozone) for an EDR-evasive Chromium profile stealer research series.
Standalone
Standalone posts
- OSINT Enrichment and Knowledge Base Enumeration with Open WebUI
Build a local Open WebUI RAG lab for OSINT on public PDFs, then enumerate the knowledge base and dump documents via API and model tools.
 Identifying and Enumerating Ollama Inference Servers
Fingerprint exposed Ollama servers: Shodan hits, Golang HTTP quirks, unauthenticated /api/tags and /api/show system prompts, plus model create and delete.
 Identifying and Enumerating vLLM Inference Servers
Fingerprinting an exposed vLLM inference server from its unauthenticated responses: its framework, version, model, routes, and calls that run without a key.
 Creating Fake Windows 11 Credential Popups with Google and Edge
Showcasing how to create fake Windows 11 credential popups only using a Chromium browser and a basic TCP listener. Research notes from Drew Alleman on...
 Dumping Enterprise Chrome Policies Using Device Management Tokens from Verbose Logs
I'll walk through post-compromise enumeration techniques to extract valuable information from verbose Chrome logs. Research notes from Drew Alleman on...
 Building a Keylogger for Windows in C++
This project is for educational purposes only. I built it to better understand how low-level keyboard input works in Windows and to prepare for writing...
 Injecting Shellcode into Processes and Bypassing Windows Defender
A blogpost showcasing code to inject obfuscated shellcode into a windows process and techniques to avoid windows defender